

Log in to two Amazon stores one after another on the same computer: Store A is asked to submit additional materials due to a category review, and three days later Store B also receives a video verification notice. Most people's first reaction is to change the IP, only to find that what's coming will still come—because IP is just one of the variables read by association determination; browser fingerprints, cookies, payment information, and operation traces are still being reused across stores.
The following answers only two things: which signals platforms like Amazon rely on to determine that multiple accounts belong to the same entity, and exactly which fields must be bound to one independent environment per store.
Scenario: Why Store B Is Also Required to Verify After Store A Is Audited
First, clarify the boundaries of the rules.
Amazon Seller Central's official statement is: generally, operate one account per region; multiple accounts may be held when there is a legitimate business need, but accounts need to remain in good standing, and a policy issue with one account may affect related accounts. This statement has two layers of meaning—multiple accounts themselves do not equal a violation, provided there is a genuine business need and compliant qualifications; account health is also not completely isolated, and risk propagates along shared variables.
So Store B being required to verify does not necessarily equal a strong technical association; it may also be a review triggered by overlapping qualifications, payment, or operation traces. There is only one direction for judgment: see exactly which fields the two accounts genuinely overlap on.
The official description of multiple accounts and the impact of association can be found at Amazon Seller Account Health NoticeVerify within it; the specific reason for the action remains subject to the account notification.
Browser Fingerprinting Principles: The platform reads not an ID, but a set of signals that can be combined
Browsers do not have such a thing as a “device ID number.” The platform’s approach is to execute scripts in the page, collect dozens of parameters, and then assemble them into a similarity vector. Each item alone is not distinctive, but combined they are very stable.
- Network and Protocol Layer: Exit IP, IP ownership and type (residential or data center range), internal and external addresses exposed by WebRTC, time zone, language preference, HTTP header order.
- Device and System Layer: User-Agent, platform, device memory, CPU logical core count, screen resolution and device pixel ratio, touch support, list of installed fonts.
- Graphics and Audio Rendering Layer: Anti-aliasing differences when Canvas draws text, GPU model and driver string returned by WebGL, floating-point differences in AudioContext, and certain media decoding capabilities.
- Storage and Behavior Layer: Cookie, localStorage, IndexedDB, cache files, as well as behavioral characteristics such as mouse trajectory, click intervals, and typing rhythm.
The key lies in consistency, not single-point disguise. Even if two Profiles change their User-Agent, if the Canvas noise seed is the same, the time zone and language combination is identical, and WebRTC leaks the same internal network segment, the calculated similarity will still be high. Conversely, if the fingerprint disguise is very clean but the proxy exit is a data center segment, this will also form another identifiable combination.
It is also necessary to distinguish isolation levels: fingerprint browsers address identity-level isolation (independent fingerprints, Cookie domains, proxy exits), and are not responsible for isolation at the process permission and file write levels.Differences in isolation principles and applicable scenarios between fingerprint browsers and sandbox browsersThere is a point-by-point comparison inside, and the applicable boundaries of the two cannot be used interchangeably.
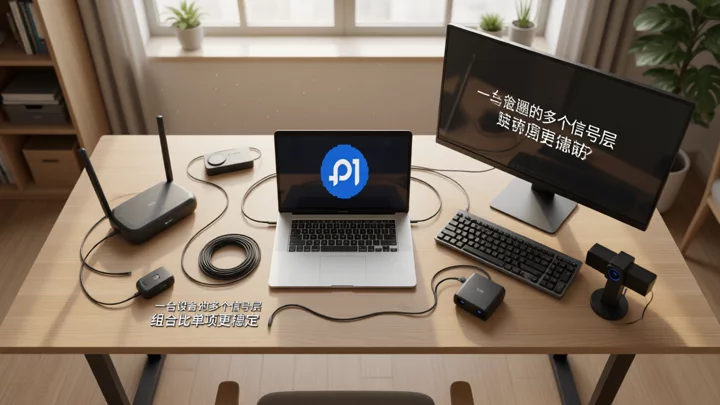 The same device is composed of multiple layers of components—network, hardware, graphics, and storage—and the platform reads the combination of these signals rather than a single parameter.
Amazon association determination: how five categories of variables are combined into evidence
Putting the above signals into operational terms gives the table below. It answers "how platforms identify multiple accounts"—not by relying on a single piece of conclusive evidence, but by multiple weak signals stacking into one chain of evidence. The "Isolation Difficulty" column indicates how quickly changes take effect, not a ranking of importance.
| Variable layer Signals possibly read by the platform Isolation difficulty Most common mistake | |||
| Identity and qualification materials | Business license, legal representative, registered address, phone, email, brand registry entity | High, mostly hard associations | Multiple stores sharing the same business license or the same registered phone number |
| Network egress | Egress IP, IP type and ownership, WebRTC exposed address, time zone | Medium | Multiple stores rotating the same batch of proxies, with IP conflicts when switching windows |
| Browser fingerprint and local storage | User-Agent, Canvas/WebGL, fonts, hardware parameters, Cookie, IndexedDB | Medium | Switching accounts only between multi-user profiles in a regular browser, with the underlying fingerprint unchanged |
| Payment and payout information | Credit card, payout account, tax information | High, mostly hard associations | Collect payments for multiple stores with a single receiving account |
| Operational behavior and personnel activity trails | Login time patterns, operating rhythm, the same person handling multiple store backends | Low, controllable | An operator using the same machine to log into the backends of three stores consecutively |
Among the five layers, two are hard associations—identity information and payment collection. Once these two layers overlap, no matter how many IPs are changed or fingerprints modified, it cannot be made up for; they can only be separated at the business structure level. The remaining three layers are soft signals, and their overlap can be significantly reduced through environment isolation and process standards. For a detailed breakdown, refer toItem-by-item analysis of IP, browser fingerprints, payment information, and operational trails in Amazon store anti-association.

Still associated after changing IP: the three most easily overlooked residual variables
Cookie and local storage remnants: If the same browser Profile has logged into store A and then store B, even if the IP is changed midway, the Cookie domain, localStorage, and cache files are still the same chain. Clearing browsing history is not the same as cleaning thoroughly; Service Worker and IndexedDB are often missed.
WebRTC bypasses the proxy to expose the real address: When the proxy only takes effect at the HTTP layer, WebRTC may still report the local internal network IP and the real public egress, which is equivalent to handing the platform an address that does not match the egress IP.
Hard association fields: The same credit card, the same payout account, the same business license, the same warehouse address, or the same set of product images and copy; such overlaps can establish a connection without the involvement of fingerprints.
The criterion is straightforward: if two stores have ever shared the same browser Profile, or the payout entity is the same, handle these two things first, then discuss proxies and fingerprints. If the order is reversed, troubleshooting will keep going in circles.
Anti-association checklist: one Amazon store corresponds to one independent environment
The core of the checklist is one-to-one correspondence, not having as many as possible. One store is bound to one environment, and anyone switching stores uses the same entry point.
- Independent browser Profile: One store, one Profile; it is forbidden to log in to two stores successively in the same Profile; include the store code in the name for easy handover verification.
- Fixed proxy egress: One store is bound to one egress IP for the long term, and the type remains stable; avoid multiple stores sharing the same proxy pool for rotation. For specific configuration ideas, seeProxy and IP egress configuration.
- Independent cookies and local storage: Storage is not shared between Profiles; after switching computers or reinstalling the operating system, do not use an old backup to restore a Profile and then log in.
- Independent payment and payout information: The payout accounts, credit cards, and tax information for each store must not overlap; this part cannot be replaced by technical means.
- Separate login personnel and permissions: Operational permissions for a store's backend should be concentrated with designated individuals, and temporary shift coverage should be documented.
- Audit trails for operation logs: At a minimum, record the time, store, Profile name, exit IP, operator, and what was done, so that you can replay what happened if problems arise.
- Device and network separation: On the same machine, switch between stores only in an isolated environment; do not casually log in to the backend with your everyday browser.
In team collaboration scenarios, this checklist also needs to be paired with account grouping and permission fields before it can be implemented,Grouping, login records, and exception handling workflow for Amazon multi-store multi-account managementFields that can be copied directly are provided; the specific standards for the environment layer, network layer, and device layer are inFour Environment Isolation Points for E-commerce Multi-Account Managementwhere they are broken down layer by layer.
 One store corresponds to one Profile, one fixed exit, and one responsible person; workstations and devices do not overlap, which is the prerequisite for the team to avoid mistakes during daily switching.
Troubleshooting Order When an Association Warning Has Appeared
Troubleshooting proceeds from the largest contamination radius to the smallest: first resolve variables that affect all stores, then handle single-store issues. Log each step once it is done to avoid repeatedly modifying the same item.
- Exit IP and WebRTC. For each store, confirm within the environment whether the exit IP matches the binding, then use the WebRTC detection page to confirm that the internal network or real public address is not leaked. Minimum fix: upgrade the proxy from the HTTP layer to the global or SOCKS layer, and switch that store to a clean exit that has not been used before.
- Cookie and Local Storage. Confirm whether the store has logged in under another Profile, and check Cookie, localStorage, IndexedDB, cache, and installed Service Worker. Minimum fix: disable the contaminated Profile, rebuild a brand-new Profile, and log in again.
- Browser Fingerprint Uniqueness. Check whether parameters such as time zone, language, resolution, and GPU strings are obviously similar across multiple profiles. Minimum fix: make each profile's fingerprint parameters follow the region of its proxy exit instead of manually piecing together a set.
- Payment and Qualification Materials. Compare receiving accounts, credit cards, legal representative information, addresses, and phone numbers item by item. Treat any overlap in any item as a hard association, and first separate them at the business level.
- Operational Behavior and Personnel Permissions. Review login logs to confirm whether the same person, during the same time period, and on the same device continuously handled multiple store back offices. Minimum fix: assign a responsible person per store, and use written handovers for shift coverage.
If the warning has already turned into an audit or video verification, environment remediation and appeal materials should be prepared in parallel: the environment side proves that each store operates independently, and the materials side proves that the business is genuine. The areas that are prone to problems after scaling from a single store to multiple stores,The Most Problem-Prone Areas in Multi-Store Operations and the 48-Hour Investigation SequenceIt can be reviewed together.
Frequently Asked Questions
Can Chrome multi-user profiles isolate Amazon stores?
Not enough. Multi-user profiles isolate cookies and login states, but the underlying Canvas, WebGL, fonts, and hardware parameters still come from the same machine and the same combination, and the network exit is not separated either. It is sufficient for everyday browsing, but using it to manage multiple stores will leave similar vectors at the fingerprint layer.
To what extent can browser fingerprints be spoofed?
What you can do is make each Profile's combination vector independent of the others and internally consistent; you cannot make it invisible. Self-contradictions such as a GPU model that doesn't match the operating system or a time zone that's inconsistent with the IP region are easier to notice than the fingerprint itself.
How should you choose between a VPS and a fingerprint browser?
A VPS answers "where this machine is," while a fingerprint browser answers "who this machine appears to be." If you install an ordinary browser on a VPS, multiple instances still share the same fingerprint; if only the fingerprint is isolated while the exit is not independent, the network layer still overlaps. Multi-store scenarios usually require the two to work together—it's not an either/or choice.
To tell whether a proxy IP is clean or has been linked, what should you check first?
First check whether WebRTC is leaking the real address, then check whether this Profile has logged into other stores, and then compare the payment and qualification materials. A clean IP only rules out one of the five layers of variables.
If you receive an association warning, should you change the environment first or appeal first?
Handle them in parallel. First, follow the order above to identify the overlapping variables and keep a record of the fixes, while preparing the materials required by the account notice. A policy issue with a single account may affect related accounts, so don't wait for the appeal outcome before dealing with the environments of the other stores.