

5 Shopify stores, 3 operations staff, and two shared computers. Half a month after the person responsible for Store B left, the person who took over discovered that the staff account bound to the backend was the departed employee's personal email—verification codes couldn't be received, and an app authorization list still had a plugin that no one recognized.
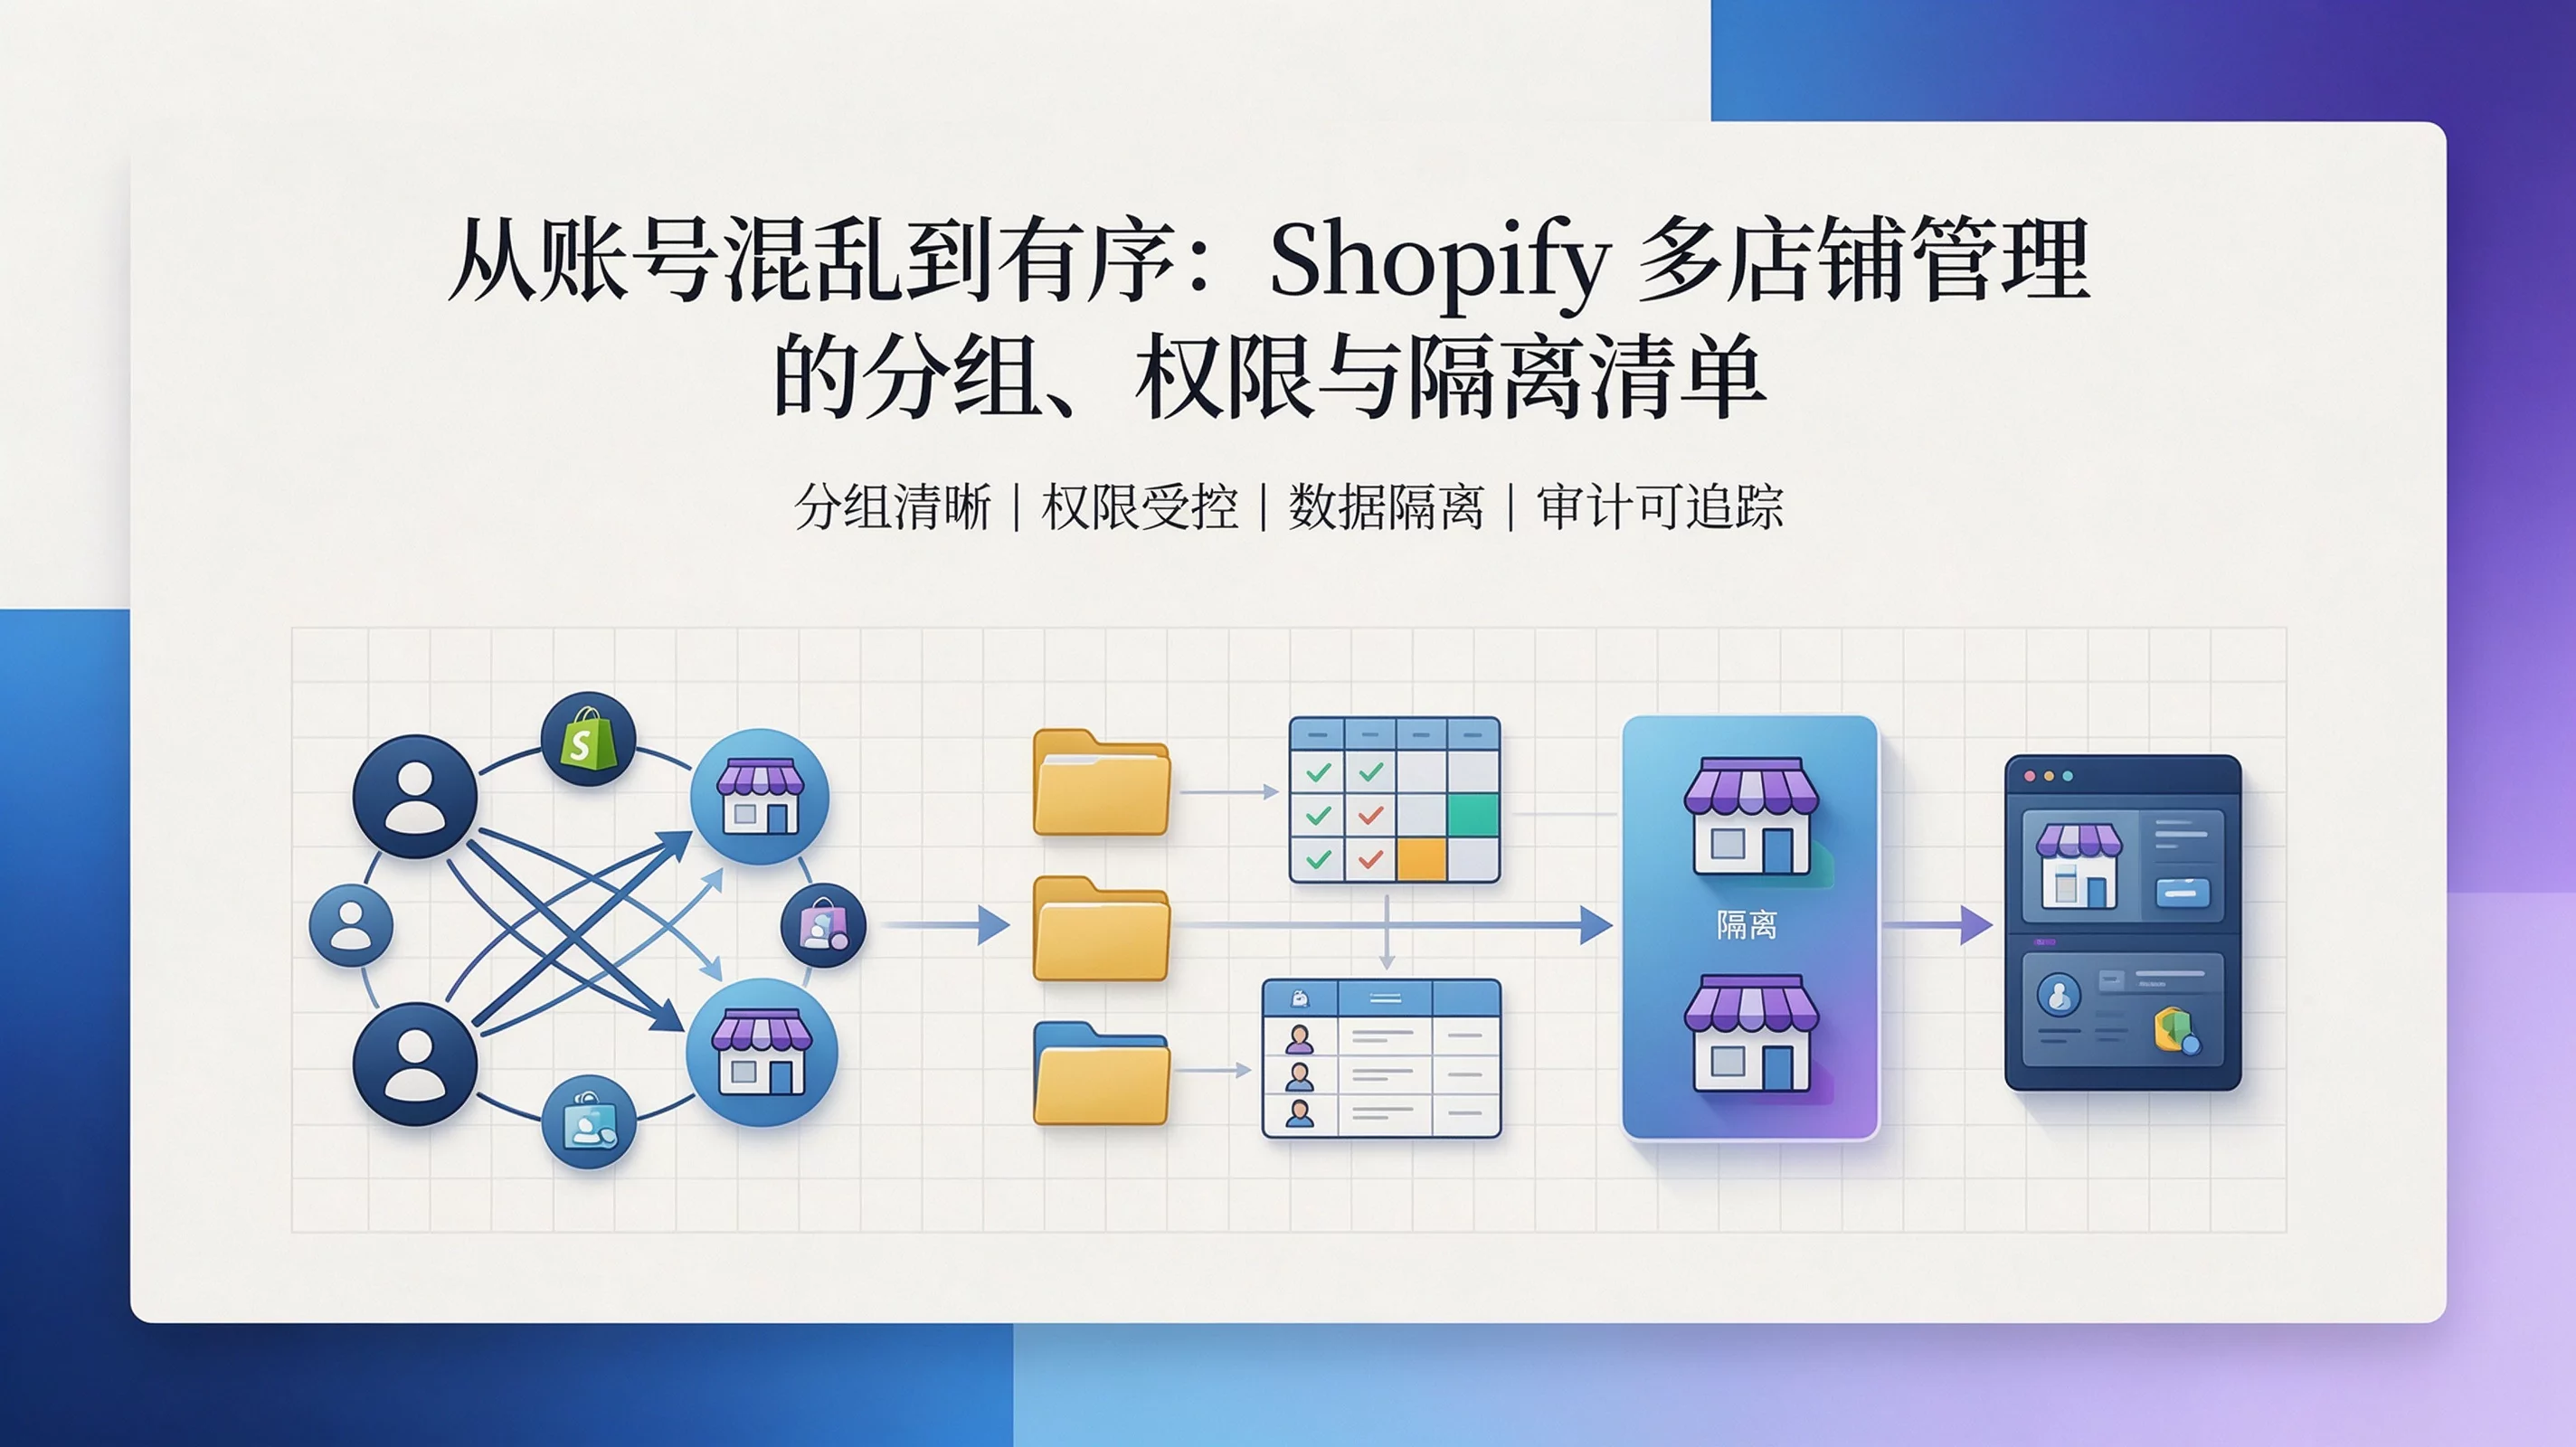
The root cause is not the number of stores, butlogin environment, staff permissions, data processesThree variables are shared across multiple stores. Below are three verifiable checklists: how to group, how to authorize, and how to isolate, along with the accompanying audit cadence.
Start by determining: chaos usually comes from three shared areas, not from having too many stores
- Shared login environment: Running multiple stores on the same computer, the same browser, and the same network exit causes Cookie, local storage, and browser parameters to contaminate each other. Traces you leave in Store A may appear in Store B's environment.
- Employee Permission Sharing: everyone logs in with the store owner's account, or one employee account is attached to multiple stores. It is impossible to tell who changed a price, and when an employee leaves, access cannot be cleanly revoked.
- Data and Process Sharing: orders, customer service scripts, and payment information are mixed together, and handovers rely on verbal communication. Once the person leaves, the store’s ownership link is broken.
The three layers are interconnected: if permissions are not locked down, environment isolation can be breached by unauthorized operations; if environments are not locked down, no matter how fine-grained the permissions are, they cannot prevent misoperations. For the specific four-layer configuration and least privilege, you can refer toA Practical Plan for Account Isolation and Team Collaboration in Multi-Store Operationsfor an item-by-item comparison.
Grouping: first by risk level, then by brand or market
Grouping determines permission boundaries and also environment boundaries. Grouping only by “who is responsible for which store” will cause permissions and environments to cross repeatedly as personnel change.
| Grouping dimension | Applicable conditions | Points to note |
|---|---|---|
| Operating entity / Risk level | Multiple entities, multiple receiving accounts, or multiple legal entities opening stores | Different entities must be kept entirely separate from environment to permissions; separating only stores is not enough |
| Brand or product line | Significant differences in brand tone, suppliers, or customer service scripts | When the same brand spans markets, do not split it too finely, or permissions will become fragmented |
| Market / Site | Multiple country sites, with significant differences in time zones and languages | Site grouping must also distinguish network egress regions |
| Operations personnel | Large team requiring per-person assessment | Use as a secondary dimension only; do not use it as the sole basis for grouping |
The recommended implementation order is: first make a cut by operating entity, then segment by brand or market within the entity, and finally attach people as "roles" rather than "groups". When an employee leaves, you only need to revoke the role, not re-partition stores. For how to organize bulk operations and permission templates, refer toConfiguration Standards and Collaboration Permission Design for Account Matrix Management.
Permissions: Least-Privilege Authorization for Shopify Staff Accounts and External Collaborators
Shopify staff accounts support assigning permissions separately by store, which is the foundation of delegated permissions. The assignable permission items are based on theShopify Official Help Centercurrent version; the following are allocation principles, not a restatement of backend features.
- Store Owner Account: Does not do daily operations. Retain only three things—billing, permission granting, and app installation approval—enforce two-step verification, and keep it in the hands of only 1 to 2 people.
- Operations: Grants order processing, product read/write, and inventory adjustments; does not grant full settings access, payments and billing, or app installation. Plugins must be requested through the submission process and installed by the store owner account.
- Customer service: View and notes on orders only, with refunds tiered by amount; customer data is read-only or granted as needed. No product deletion rights, and no unlimited discount creation rights.
- Finance: Billing, payment transaction records, and reports — view access is enough; there is no need to enable product and order editing permissions.
- External development or marketing collaborators: Create a separate staff account whose permissions cover only the collaboration scope; never enable domain, payments, or settings, and disable it on the day the collaboration ends.
Three easily overlooked actions: enforce two-step verification for everyone; run offboarding in the order of “disable first, then transfer domain and payment ownership, and finally delete”; clean up app authorizations once a quarter by unbinding third-party apps that are no longer in use.
Isolation: What must never be shared on the same computer
- Browser fingerprints and device parameters: A separate environment configuration for each store, including User Agent, screen and time zone, fonts, WebGL, and other parameters. Two stores sharing one browser configuration is equivalent to voluntarily giving up isolation. For selection and initial configuration, seeConfiguration methods for environment isolation, proxy configuration, and account management.
- Proxies and Network Egress: One store, one egress; the egress region must be consistent with the store's registration location and daily login habits. Multiple stores sharing one IP, or frequent egress changes, will create recordable behavioral characteristics.
- Cookies and Local Storage: Each environment independently stores cookies, localStorage, IndexedDB, and cache. Clearing cookies only clears one layer; it cannot clear device parameters.
- Login Behavior Cadence: Do not use scripts to log in to all stores sequentially within a few minutes; stagger the timing and maintain natural intervals between operations.
- Recovery Information and Payment Information: Each store should have its own email address, phone number, and verification channel; payment accounts should be configured according to the entity and platform requirements, and do not use one set of information across all stores.
Regarding “Is clearing cookies enough?”: No. Cookies are only part of the identity layer; device parameters, network egress, and local storage are other layers, and the principle boundary is inFingerprint Browser Identification Principles and Isolation Boundarieswhich provides a layer-by-layer explanation.
From checklist to execution: a weekly 10-minute and monthly 30-minute audit rhythm
- Weekly: pull the login records for each store once, and confirm there are no cross-environment logins — logging into Store B's backend from Store A's environment is the most common breach point.
- Weekly: check whether proxies or network egress are reused, especially when adding a new store.
- Weekly: record employee permissions and app authorizations added or changed this week.
- Monthly: reconcile the employee permission list against actual roles, and remove permissions that are no longer needed.
- Monthly: clean up app authorizations and check two-step verification coverage.
- Monthly: check offboarding handover status, and confirm no accounts are still bound to the departing employee's email or phone.
When an anomaly is detected, isolate first and then investigate: switch the suspicious store alone to an independent environment and egress, freeze high-risk actions such as bulk price changes and bulk listings, then review login records and permission changes. Changing the password first does not solve the problem; the sharing at the environment level remains. For the troubleshooting order when running multiple stores, refer toThe Most Problem-Prone Areas in Multi-Store Operations and How to Address Them.
Frequently Asked Questions
Now that Shopify staff permissions are granular, is browser environment isolation still needed?
Yes. They govern different things. Staff permissions govern "who can do what," while environment isolation governs "where actions originate from." If the same person uses the same browser to log into two stores, no matter how granular the permissions are, cookies and device parameters are still shared.
If the same legal entity or the same payment receiving account opens multiple Shopify stores, is that considered an association?
It cannot simply be equated with an association. The platform judges based on multiple signals such as entity information, business behavior, and login environment. For specific rules, refer to official policies. Also, do not use environment isolation to conceal entity information that should be independent.
Is clearing only cookies and cache enough?
Not enough. What gets cleared is only part of the identity layer; device parameters, local storage, network exit, and login behavior are still there. Either establish an independent environment for each store, or accept that these variables continue to be shared.
If a store has already been spot-checked or restricted, should you change permissions first or switch environments first?
Isolate first. Switch the store to an independent environment and exit, pause cross-store bulk operations, then review login records, permission changes, and app authorizations to identify the cause, and handle it according to the appeal path specified in the platform notification.