

3 people manage 6 TikTok Shop accounts. One day, one of the accounts receives an environment anomaly alert, yet no one on the team can clearly say who logged into this account in the last 72 hours, on which computer, and through which network egress. This situation is usually not caused by the number of accounts, but by several variables being repeatedly shared: the same machine, the same broadband connection, the same login password, and the same operator.
In fact, only three things need to be settled: which environment a TikTok Shop account corresponds to, who has the right to enter that environment, and how to cleanly hand over control when people change. Below, we provide judgment criteria and directly fillable fields based on these three things.
Account, Environment, Owner: First Define a Non-Shareable Boundary
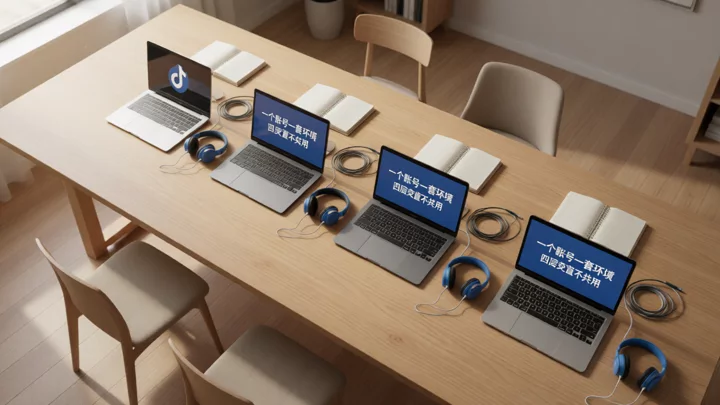
The rule is: one account is bound to one independent browser environment and assigned one owner. The owner is not the only operator—collaborators can be authorized in through official roles—but they are the only person responsible for this account's environment configuration and permission changes.
To verify whether the rule has been implemented, use one test: pick any account, and you can state within two minutes the environment ID it is bound to, as well as the person and time of the most recent login. If you cannot, the boundary still exists only in words.
When sharing is truly necessary (for example, temporary shift cover), the sharing itself must leave a trace: who borrowed which environment, from when to when, and whether the session was cleaned up afterward. Unrecorded tacit sharing is exactly where the cause cannot be found after the fact.
Environment Isolation: One Environment per TikTok Shop Account—What Specifically Needs to Be Isolated
A platform's determination of account association is not a single switch but the result of a combination of multiple signals, so isolation must be done in layers and cannot be achieved by simply changing the IP. The following four layers must at least be independent to the extent that they are not reused across accounts.
- Network Egress: Each account must be bound to a fixed proxy IP, and one egress must serve only one account. Do not put all the company's stores under the same office broadband. The proxy's registration region should match the store profile and receiving region; frequent region hopping is more suspicious than a stable egress.
- Browser Fingerprint: Use an independent Profile for each account, and do not reuse device parameters, time zones, or languages across accounts. Multiple windows and incognito mode in a regular browser do not count as isolation; they share the same underlying parameters. For configuration standards for independent Profiles, refer toEnvironment Isolation and Proxy Configuration for Fingerprint Browsers.
- Cookies and Local Storage: Profiles each store session data independently. The most critical rule is that logging into two accounts sequentially within the same environment is prohibited—changing accounts requires changing environments, not just clicking logout.
- Identity Information and Payment Collection: Store qualifications, linked email addresses, phone numbers, and receiving accounts must not be cross-reused; the same payment recipient serving multiple stores is equivalent to concentrating risk at a single point.
- Operational Behavior: Stagger the pace of batch listing, price changes, and customer service replies by account as much as possible, to avoid several accounts performing exactly the same actions within the same minute.
Make this boundary clear: doing isolation well reduces environment-level reuse risk, but it does not mean an account will definitely not be penalized by the platform; ultimately, account notifications and official policies prevail. For a more detailed layered breakdown, seeKey Points of Four-Layer Environment Isolation for E-commerce Multi-Account Management.
Login permissions: Use official roles to assign access; do not share the main account password.
When there are many accounts, the most common lazy shortcut is to send the main account password to a group chat. This simultaneously breaks two things: environment isolation (who logs in from which environment becomes uncontrollable) and permission auditing (operational incidents cannot be traced).
TikTok's official approach is to assign asset permissions by role. Ad and business assets can go through Business Center for centralized management, and the official roles and permissionsDivide them into administrator, standard member, finance, and other types, and explicitly recommend assigning members access scopes that match their positions based on asset permissions, avoiding shared login credentials. The same applies to the store side: prioritize sub-accounts or role authorization rather than handing over the main account.
Official roles determine whether one can get in, while the internal permission table determines what one can do after getting in. This table must contain at least the following fields; if any is missing, there will be gaps during handover:
| Field | What to fill in | Purpose |
|---|---|---|
| Account | TikTok Shop account or store identifier | One-to-one correspondence with official assets |
| Environment ID | Profile ID + bound proxy egress | Locate login environment |
| Official role | Administrator / Standard Member / Finance | Determines the scope of visible assets |
| Internal operational scope | e.g., listing only, price changes, and withdrawals | Restrict actions outside permissions |
| Responsible person | Name of the sole responsible person | Environment and permission changes require their confirmation |
| Validity period and approver | Start and end dates + approver | Temporary permissions are automatically reviewed upon expiration |
Permissions do not need to be changed every day, but every change must be recorded in this table. For how roles correspond to job responsibilities, refer toPractical Division of Responsibilities for Multi-Store Account Isolation and Team Collaboration.
Handover Process: Routine Handoffs and Offboarding Recovery, with Fixed Checkpoints
Handover errors are often not because the process is too complex, but because the order is wrong: changing the password first and cleaning up the environment afterward leaves the old session in the original Profile. Always follow the order below:
- Verify account-to-environment binding: Confirm which Profile and which proxy exit the account being handed over maps to, and write this into the handover record.
- Log out of the session and clean up the environment: Actively log out within the corresponding Profile and clear Cookies and local storage; closing the window alone does not count as complete.
- Confirm the proxy exit: Check whether the exit IP bound to that Profile matches the registered one and whether it has been temporarily switched.
- Adjust permissions: Change the role or asset authorization in the official backend, and update the internal permission table accordingly.
- Archive the record: Write down the last operation time, current status, and whether there is any abnormal prompt, and have the successor confirm.
The difference between routine handoffs and offboarding recovery lies in the scope of revocation: In addition to completing the above five steps, offboarding also requires handling the linked email, phone number, proxy ownership, and approval relationships, and clearing all of the person's environment access permissions, rather than merely removing them from the group.
When an association warning appears, investigate from the largest contamination radius to the smallest.
The investigation order does not start with the easiest thing to change, but with the one with the greatest impact; otherwise, you will repeatedly waste effort.
- Shared exit and environment: First check whether the exit IP of the warned account also serves other accounts and whether the environment has been used by multiple people. The minimum remediation action is to switch to a dedicated exit and, within 48 hours, have only the responsible person sign in, and observe whether the warning continues to appear.
- Cookie and local storage remnants: Confirm whether this Profile has ever signed in to other accounts. The minimum remediation action is to clear the session and sign in again once.
- Permission sharing and operation trails: Check the internal permission table to see whether there have recently been operations by someone other than the responsible person and whether several accounts have performed synchronized bulk actions. The minimum remediation action is to revoke temporary permissions.
- Identity data reuse: Check whether the bound email address, phone number, and payout information are duplicated with other accounts. This layer is the hardest to change and also requires the most advance planning.
During the 48-hour observation period, do not make other adjustments; otherwise, you cannot determine which layer's remediation took effect. If the warning persists, follow the guidance in the platform account notification and keep operation records. For the steps in routine multi-store maintenance that are prone to problems, you can refer toCommon failure points when running multiple stores at the same timeCheck them one by one.
Common questions
If two people manage 3 TikTok Shop accounts, does each account still need an independent environment?
Yes. A small number of accounts does not mean the environment can be shared. If two people share one computer to log in to three accounts, it is equivalent to putting all three accounts under the same set of Cookies and the same egress. The minimum requirement is to create a Profile per account, assign clear responsibility to specific individuals, and document any sharing.
What is the difference between using official role-based authorization and sharing the main account password?
Official roles determine which assets members can view and operate, and revoking permissions only requires an adjustment in the backend; sharing the password, however, makes all operations fall under the same identity, so there is no way to trace who did what. Official guidance also recommends assigning asset permissions by job role and avoiding shared login credentials.
Is logging out alone enough during handover?
No. After logging out, Cookies and local storage may still remain. The correct approach is to log out within the corresponding Profile and clear the session, then confirm that the proxy egress matches the registration, and finally adjust permissions accordingly and archive the records.
If the proxy is fixed, what should be done when traveling for business or switching networks?
Prioritize connecting remotely back to the team's unified office environment for operations; do not log in directly to store accounts on an unfamiliar network. If off-site operation is unavoidable, confirm the environment and proxy ownership clearly before the trip, and after returning, check whether the egress IP has been changed according to the handover process.
How do you determine whether an account association warning is an environment issue or an operational issue?
First check whether the egress IP and environment are shared by multiple accounts, then check the internal permissions table for recent operations by non-owners or batch actions synchronized on which date. Within 48 hours, change only one layer and observe; do not adjust multiple items at the same time, otherwise you will not be able to pinpoint the issue.